TOP

Active directory assessment 

Securing the Keys to Your Organization

Active Directory controls who can access your data and how privileges are distributed—making it the primary target in nearly every major breach. STSG’s assessment is a forensic-grade audit that surfaces the hidden pathways attackers use to escalate privileges and take control of your domain.

24/7

Monitoring & Support

99.9%

System Uptime Goal

Proactive

Prevent Issues Before They Happen

Secure

By Design

//WHY IT MATTERS //

The STSG Advisory Guarantee:
Strategy Without Validation Is Just Hope

We don't just hand you data — we hand you a roadmap. Every engagement rests on three commitments that turn analysis into executive action.

List

Framework-Driven

Every engagement is benchmarked against globally recognized standards — NIST CSF, ISO 27001, and CIS Controls — so your posture is measured against proven baselines, not opinion.

List

Business-Language Reporting

We translate technical findings into language the boardroom understands, so leadership makes security decisions with confidence—not lost in jargon.

List

Actionable, Not Academic

We don't just hand you data — we hand you a prioritized roadmap. Every finding comes with a clear, ranked next step, not just a list of problems.

// WHAT'S INCLUDED //

What's Included in a Risk Assessment

Immutable architecture, air-gapped isolation, hybrid cloud redundancy, application-aware capture, and nightly verification — combined so a pristine copy of your data always survives.

List

The 3-2-1-1-0 Backup Standard

Three copies, two media types, one off-site and one offline immutable copy — verified with zero errors through automated recovery testing on every cycle.

Explore More
List

Immutable Storage & Logical Air-Gapping

WORM object-lock and logical air-gapping create a recovery environment fully isolated from production — untouchable even by a compromised administrator.

Explore More
List

Cloud Disaster Recovery & Hybrid Redundancy

On-site flash storage delivers rapid file and VM recovery, while simultaneous replication to encrypted cloud regions protects against local and regional outages.

Explore More
// WHAT'S INCLUDED //

What's Included in an Active Directory Assessment

Attack-path mapping, credential hygiene, configuration hardening, and recovery planning — combined so the identity layer that underpins everything can't be quietly turned against you.

List
01

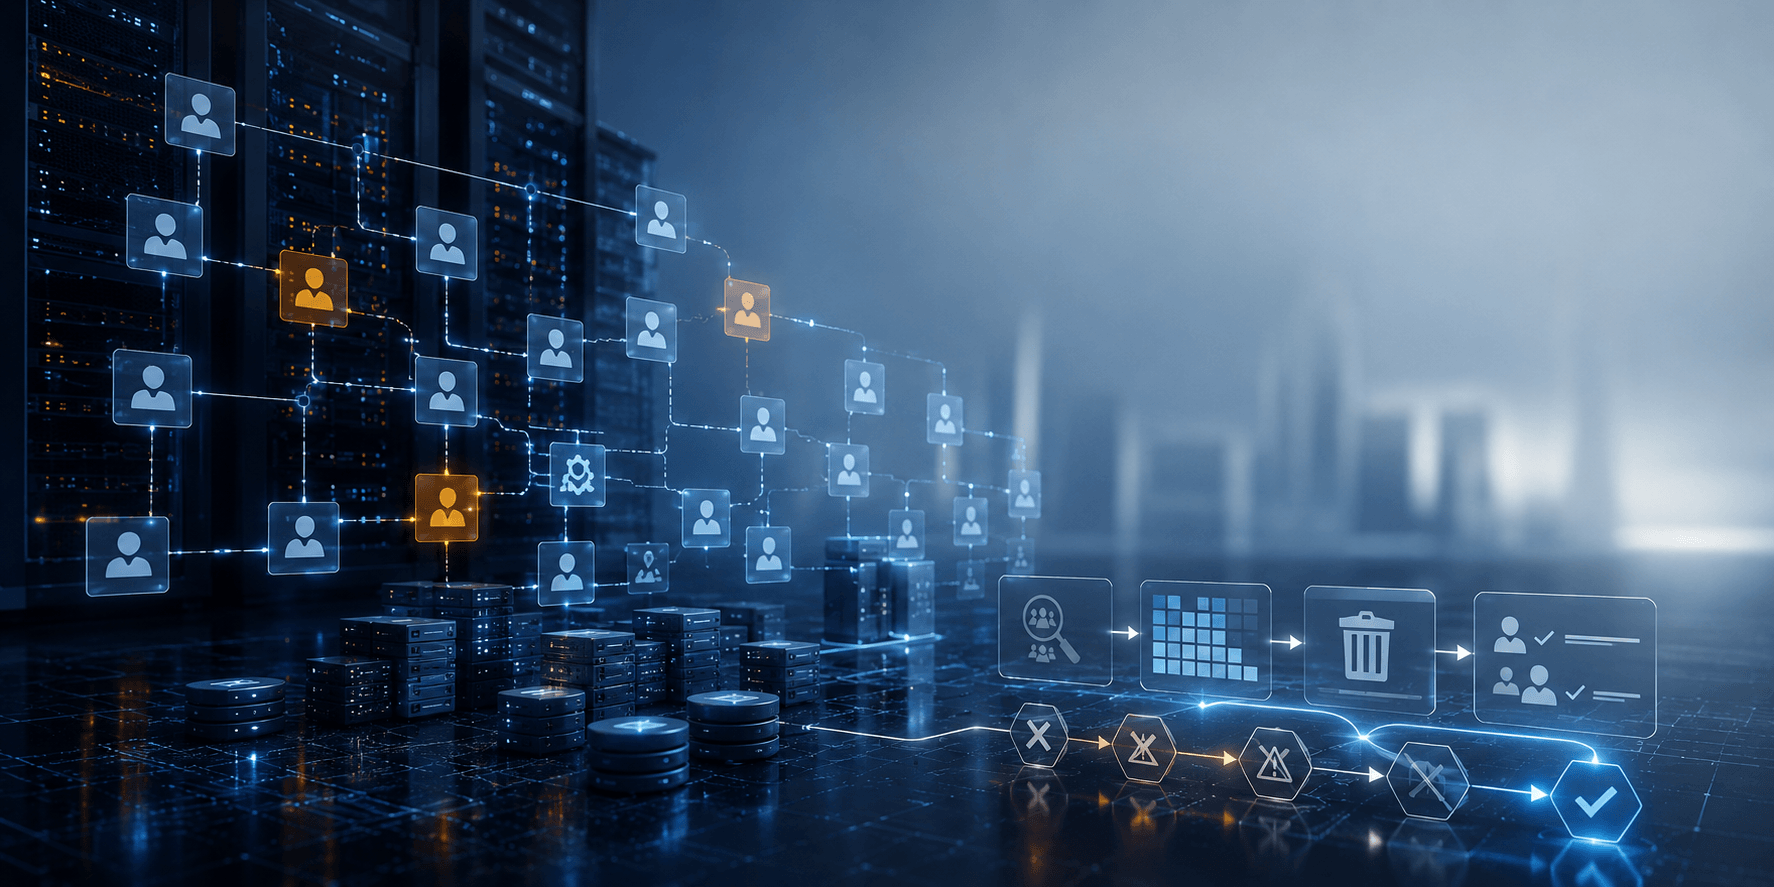
Attack Path Analysis & Privilege Escalation Mapping

We visualize every path an attacker could take from a standard user account to Domain Admin — including hidden admins outside the Domain Admins group that can still reset admin passwords.
List
02

Account Hygiene & Credential Security

We audit your identity repository for orphaned accounts and service accounts with long-unchanged credentials, and flag legacy protocols like NTLMv1 and LLMNR with a safe decommissioning roadmap.
List
03

Group Policy & Configuration Hardening

Misconfigured GPOs silently weaken your posture across every workstation. We confirm settings are correctly enforced and identify Kerberoasting-vulnerable service accounts.

List
04

Detection Capability & Recovery Planning

Even a hardened AD can be targeted. We audit Domain Controller security and your forest recovery plan — confirming immutable backups and a documented rebuild process.


// Industries We Support //

Advisory Tailored to Your Sector

We frame every assessment and advisory engagement around the compliance realities and threat models of the industries we serve.

List

Healthcare

HIPAA requires proof, not promises. Our assessments and pen tests protect patient records and clinical systems while satisfying auditors.

List

Financial Services

PCI-DSS compliance demands regular, documented testing. We validate payment systems and cardholder data environments against real attacker logic.

List

SMBs

Limited IT staff doesn't mean limited risk. We deliver enterprise-grade testing scaled to fit small and mid-sized budgets and teams.

List

Manufacturing

OT and IT convergence opens new attack paths. We validate industrial control systems and production networks without disrupting operations.

List

Education

Distributed campuses and research data create a wide attack surface. We help schools and universities validate defenses across every connected system.

List

Non-Profit

Donor data and lean security budgets are a risky mix. We help mission-driven organizations find gaps before attackers exploit trust.

// How We Work //

A Proven Process for Reliable Advisory

Every advisory engagement follows the same disciplined, transparent process — so you always know the next step and the reason behind it. It's the same proven approach featured across the STSG site. 

Discover

We learn your business, your critical assets, and the risks that matter most to leadership.

Assess

We analyze your posture against recognized frameworks, surfacing gaps and quantifying risk.

Plan

We translate findings into a prioritized roadmap mapped to business impact and budget.

Implement

We guide remediation and re-check, turning strategy into measurable improvement.

List
List
// More Than Managed IT //

Full-Spectrum Technology Solutions

From cybersecurity and cloud to infrastructure and consulting, STSGinc delivers end-to-end technology solutions that power your business forward.

  • Cybersecurity Built In
  • Cloud, Microsoft & Infrastructure Expertise
  • Strategic Guidance, Not Just IT Support
List

Your Identity Is Your Most Valuable Asset — Protect It With STSG

Identity is the new perimeter. If AD falls, no firewall can save your data.
// FAQ //

Active Directory Questions? We've Got Answers

The questions we hear most about building a human firewall.

Can’t locate the answers you need?

We work with a trusted network

Ask Your Question: contact@stsg.com

Because it controls who can access what across your entire environment, compromising AD lets an attacker effectively own the domain—which is why it's targeted in nearly every major breach. Our forensic-grade audit surfaces the hidden paths they'd use to get there.

It's a visualization of every route an attacker could take from a standard user account to Domain Admin. We map those chains — including hidden admins outside the Domain Admins group that can still reset admin passwords — so you can cut them before they're used.

We're careful to avoid that. When we flag legacy protocols like NTLMv1 and LLMNR, we provide a safe decommissioning roadmap, and we validate Group Policy changes so hardening strengthens posture without disrupting production.

We audit Domain Controller security and your forest recovery plan for exactly that scenario, confirming you have immutable backups and a documented, tested rebuild process that will hold up under real pressure.